7 Reasons Why 2-Step Verification Is Always Worth the Extra Effort

We log in to dozens of online accounts each day and unlock everything from offices to bank accounts through a combination of physical and digital authentication. Like a locked box inside a safe, many of these authentication processes ask us to identify ourselves more than once.
Our overcrowded schedules make us wonder if the time spent on extra security is really necessary. Is 2-step verification worth it?
What is 2SV?
2-step verification (2SV) is a security process that requires people to successfully identify themselves in two different ways before they can gain access to a secure system. 2SV enhances security by asking people to provide something beyond just their password—something that hackers or password thieves are unlikely to have. Sensitive processes like ATM transactions have been using 2SV for decades to protect consumers.
In the physical world, this double-lock concept has been practiced for centuries, as visitors often identified themselves twice when entering secure buildings or forts and presented guards with identifying documents or secret codes along the way. This idea is now commonly seen in the digital world: codes are sent to devices to supplement password security, or a combination of facial recognition and a PIN code is required to unlock a smartphone.
How does 2SV work?
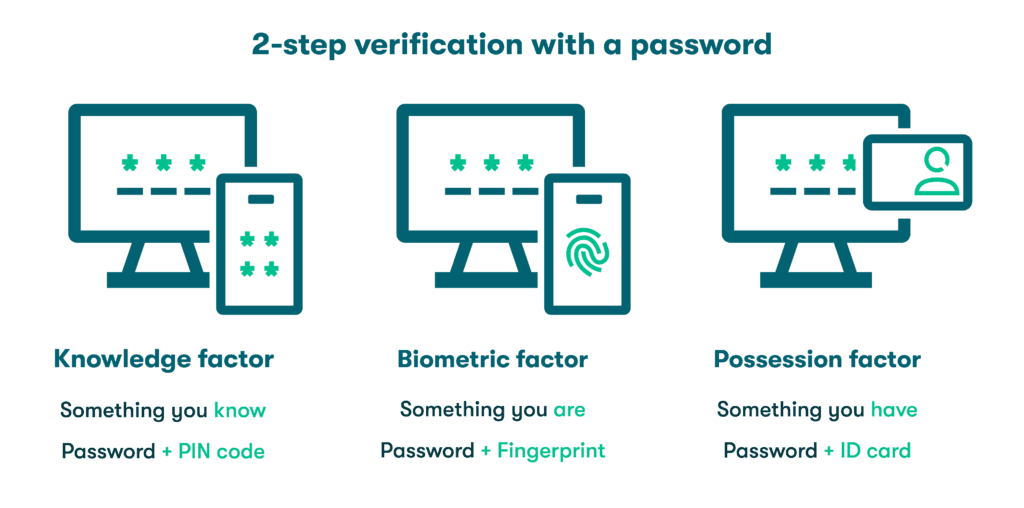
2-step verification is more effective than traditional single-factor verification that only considers a username and password combination. To make the verification steps more challenging for outsiders or hackers to replicate, 2SV draws on authentication factors from three different categories:
- Knowledge factors: The most commonly used authentication factors today are knowledge factors, or something you know. Passwords are the most familiar knowledge factors, but this category also includes PIN codes or answers to security questions, such as your mother’s maiden name or the make of your first car. Ideally, a knowledge factor is something only you know.
- Biometric factors: Inheritance or biometric factors are based on the unique genetic characteristics of each individual. This includes fingerprints, facial recognition, and even vocal characteristics that no two people on earth share. Artificial intelligence and computing capacity continue to bring new biometric factors like retinal scanning into the fold while improving our ability to discern minor differences between individuals and weed out fraud.
- Possession factors: Possession factors refer to physical items you have that no one else would possess under ordinary circumstances. Obvious examples are smartphones and thumb drives, but possession factors also include objects like security keys and ID cards that we tend to keep close to protect them from loss or theft.
Difference between 2SV and 2FA
2-step verification (2SV) and 2-factor authentication (2FA) are often used interchangeably, but there are some subtle differences between the two practices. 2-step verification (2SV) requires two sequential verification steps, such as a username/password combination followed by a code. Note that the password and code are both considered knowledge factors.
On the other hand, 2-factor authentication (2FA) utilizes two distinct authentication factors that must be from two different categories, such as knowledge and inheritance. An example would be a password followed by a fingerprint scan on your phone.
Since 2FA uses two authentication factors, it also meets the definition of 2SV. However, the opposite is not always true since 2SV doesn’t necessarily use two different categories of identifiers.
7 reasons why 2SV is worth it
Adding an additional layer of verification provides reinforcement to a standalone password. 2SV makes it more difficult for malicious actors to access private accounts because they must obtain not one, but two forms of authentication. Using authentication factors from multiple categories (such as knowledge + possession or knowledge + biometric) further enhances security by requiring unrelated information that’s not easy to guess or replicate.
Furthermore, 2SV has become so commonplace that we don’t often realize we’re using it. Think of a resident entering an apartment building or housing complex gate by entering a secret code. They will still need a second sequential factor (key) to unlock their front door. 2SV has become an essential security practice by offering:
- Protection from hacking and data breaches. Many common hacks and scams rely on compromised or stolen passwords to gain unauthorized access. Brute-force attacks use algorithms to guess at passwords, while credential stuffing attacks attempt to find matching accounts for passwords purchased on the dark web. Neither of these hacking tactics alone has any impact when 2SV requires the hacker to produce additional knowledge, possession, or inheritance factors.
- Protection from phishing. The social engineering tactic known as phishing utilizes emails that appear to be from reputable sources to trick unsuspecting recipients into sharing their credentials, revealing personal information, or clicking on unsafe links. Like other malicious hacking tactics, phishing attacks are used to illegally obtain user credentials that can be sold or exploited. A second identifier can reduce the likelihood of a successful phishing attack.
- Identity protection. Some identities are stolen for the purpose of stealing money and opening fraudulent accounts, while others involved medical or legal information used for impersonation scams. 2-step verification provides protection from identity theft by further restricting access to accounts like social media and email that reveal volumes of personal information.
- Mobile device security. Protecting mobile devices has taken on new importance due to the mobility of today’s workforce and bring your own device (BYOD) policies. 2SV is an effective way to keep the company and personal data stored on your mobile devices safe, even when a device is lost or stolen. Inheritance factors such as fingerprints and facial recognition have been well received by mobile device users based on a combination of security and ease of use.
- Privacy protection. Data privacy laws and policies help us to control how our own personal information is collected, stored, and shared while ensuring companies take steps to prevent consumers from being hacked. By providing a secondary authentication gate, 2SV helps to secure data privacy for businesses and consumers. Along with data encryption and password managers, 2SV is viewed as one of the most important and effective data security tools available.
- Account recovery. When you’re locked out of an account, 2SV can become a useful recovery method. A secondary factor, such as a code sent through an email or text, can be used to reset your password and recover the account. During the recovery process, 2-step verification is applied in reverse order when the code is entered first, followed by the recreated password.
- Maintaining regulatory compliance. Strengthened authentication is an important regulatory compliance element that weaves its way through consumer privacy, data protection, and payment handling regulations established by the PCI DSS security standard. Complying with applicable regulations can be a driving factor for implementing 2SV, although many companies have already realized the benefits of this practice for themselves and their customers. For mid-market companies operating under SOC 2, HIPAA, or PCI DSS, this compliance driver is worth examining in more detail: each framework treats strengthened authentication differently, and knowing exactly what each one requires (and what it does not yet require) matters for audit preparation.
How 2SV and MFA requirements show up across SOC 2, HIPAA, and PCI DSS audits
Larger companies are frequently subject to more than one compliance framework simultaneously: a SaaS company processing payments may need to satisfy SOC 2 for enterprise customers, PCI DSS for card processing, and, in some cases, HIPAA or another healthcare regulation if health data passes through any part of the product. Understanding how each framework treats multi-factor authentication is essential for building an audit-ready security posture because the requirements are not identical.
PCI DSS 4.0: An explicit, mandatory MFA requirement
Of the three frameworks, PCI DSS is the most specific and prescriptive about MFA. PCI DSS version 4.0 introduced Requirement 8.4.2, which mandates multi-factor authentication for all access into the cardholder data environment (CDE), not just remote or administrative access, which was the narrower scope under the prior version 3.2.1.
Requirement 8.4.2 was published as a future-dated requirement, treated as best practice through March 31, 2025. As of that date, it became a mandatory requirement for any organization assessed against PCI DSS 4.0. Alongside it:
- Requirement 8.4.1 requires MFA for all non-console administrative access into the CDE.
- Requirement 8.4.3 requires MFA for all remote network access originating from outside the organization’s network that could reach the CDE, covering both employees and third-party vendors.
- Requirement 8.5.1 sets technical standards for how MFA systems must function: resistance to replay attacks, no bypass mechanism for any user (including administrators) without a documented and time-limited exception, and a requirement that at least two distinct factor types be used with all factors succeeding before access is granted.
For a business handling cardholder data, this means MFA is no longer optional or limited to admin accounts. It must be enforced for every path that reaches the CDE, evaluated by a Qualified Security Assessor (QSA) as part of the PCI DSS assessment.
SOC 2 Type II: MFA as audit evidence, not a named requirement
SOC 2 works differently. It does not name specific technologies or prescribe a specific control like “implement MFA.” Instead, SOC 2 evaluates an organization against the Trust Services Criteria, which include access control principles: broadly, that the organization restricts logical access to authorized users and can demonstrate how that access is granted, modified, and revoked.
In practice, MFA has become the expected way organizations satisfy these access control criteria. Auditors reviewing a SOC 2 Type II report look for evidence that access to sensitive systems is authenticated with more than a password alone, and the absence of MFA (particularly on admin accounts, internal applications, and systems handling customer data) is one of the most common findings that leads to a qualified opinion rather than a clean report.
For a company preparing for its first SOC 2 audit, the practical takeaway is that MFA should be treated as a near-mandatory control even though the SOC 2 framework itself does not use the words “multi-factor authentication” as a checklist item. The auditor’s expectation functions the same as a requirement in practice.
HIPAA: Access controls are required today; an explicit MFA mandate is still pending
For U.S. organizations, HIPAA’s current Security Rule requires covered entities and business associates to implement access controls and audit controls for any system that touches electronic protected health information (ePHI). This requirement is in effect today and has been for years, but the current rule does not name multi-factor authentication specifically as a mandatory control. Historically, HIPAA has used an “addressable” versus “required” distinction for many implementation specifications, giving organizations some flexibility in how they satisfy the underlying access control standard.
This is changing, but not yet finalized. In January 2025, HHS’s Office for Civil Rights published a Notice of Proposed Rulemaking (NPRM) that would update the HIPAA Security Rule to explicitly require multi-factor authentication for interactive workforce access to ePHI, eliminating the addressable/required distinction for MFA and several other controls. As of mid-2026, this update has not been finalized: HHS has indicated the rule will not see final action until at least July 2027.
The practical guidance is that MFA is not yet an explicitly named HIPAA requirement, but implementing it now satisfies the current access control standard more robustly than a password alone, and positions the organization ahead of the pending rule change rather than scrambling to comply once it is finalized.
What this means for your compliance posture
Across all three frameworks, the practical direction is the same even though the legal specificity differs. Strong authentication beyond a single password is either explicitly mandated (PCI DSS), functionally expected by auditors (SOC 2), or required at the access-control level with MFA increasingly the default way to satisfy it (HIPAA today, and explicitly tomorrow under the pending rule).
This is consistent with the broader compliance discussion in What a Secure System Is and How to Implement It in Your Business, which identifies SOC 2 Type II, ISO 27001, HIPAA, and GDPR as the frameworks most commonly requiring demonstrable credential security controls at enterprise scale. MFA sits at the center of that control set. It's one of the few security measures that maps cleanly across every framework a mid-market company is likely to face, whether the specific requirement is named explicitly or implied through an access control standard.
For a security team managing this across multiple frameworks simultaneously, the practical path is a business password manager with built-in MFA support and admin visibility into enrollment, so the security team can demonstrate, with an audit trail, that MFA is enforced across every account it needs to cover, rather than confirming it account by account before an assessor arrives.
Dashlane’s admin console provides this visibility for enrolled employees, and its access log data can support the audit evidence auditors request during SOC 2, PCI DSS, and HIPAA assessments.
Examples of 2SV in use
2-step verification is all around us and can even be found in unsuspecting locations like supermarkets, offices, and vehicles. Examples of common 2SV applications include:
- ATM transactions: Using a debit card to bank or shop might not seem like an example of 2SV until you examine the process. First, you insert the card into a reader to begin the transaction. The card is a possession factor since it’s something tangible that only you possess. The PIN you use to complete the transaction is a knowledge factor that confirms your identity.
- SMS codes: A familiar verification process common to both 2SV and 2FA are the text message codes so often required to gain account access, especially for banking, government service, and other secure websites. After providing your password, you complete a second verification step by entering a four- to six-digit code received in a text or email.
- Push notifications: Push notifications are the pop-up messages that appear on a person’s device to remind them when additional action is required. To use push notifications, the person will need to register their device or install an appropriate app. Since the authentication is sent to the device, rather than through text or email, push notifications are considered a possession factor.
- Authenticator apps: An authenticator app can be installed on a mobile device to support 2SV by generating security keys within a specific time window. Time-based algorithms generate random codes that time out quickly, so there’s no risk of lost or stolen codes. Much like the other commonly used secondary factors, authenticator apps are typically used in conjunction with traditional passwords.
- One-time passwords: A one-time password (OTP) works much like an alphanumeric version of a text message code, since it can only be used to access an account once and has no value after the login is completed. Time-based one-time passwords (TOTPs) might be active for as little as 60 seconds before a new OTP is needed. As a highly secure knowledge factor, one-time passwords are also used during the account recovery process.
- Biometric methods: Biometric inheritance factors and other passwordless authentication methods are quickly gaining momentum as the technology improves. Biometric methods are viewed by security experts as a strong, long-term 2SV option that reduces data breaches and improves the user experience.
- Security questions: The make of your first car and name of your elementary school might be etched in your memory for a good reason. Security questions are regularly deployed as a 2SV tool, especially when people are logging in from unfamiliar devices or locations and security is ramped up. Since a password/security question combination leverages two knowledge factors, it provides an example of a 2SV authentication process that does not qualify as 2FA.
How Dashlane uses 2SV to protect your data
Dashlane’s patented security architecture uses the benefits of 2SV to protect your data in many important ways. When you log on to a new device using your Master Password, we send a code to your email address to complete the 2SV process.
Dashlane provides secure, encrypted vaults for password storage and sharing that protect all your data. Features, including a Password Health score and a VPN, improve your password hygiene, while Dark Web Monitoring scans the depths of the internet for your credentials and alerts you if they’ve been impacted. Patented zero-knowledge architecture ensures that no one, including Dashlane, can access your unencrypted passwords and personal information.
Frequently asked questions
Does PCI DSS require multi-factor authentication?
Yes, explicitly. PCI DSS 4.0 Requirement 8.4.2 mandates MFA for all access into the cardholder data environment, and this requirement became fully mandatory on March 31, 2025, after a transition period as a best practice. Additional requirements (8.4.1 and 8.4.3) mandate MFA for non-console administrative access and remote access respectively. Organizations handling cardholder data should treat MFA as a non-negotiable control across all three access paths.
Does SOC 2 require multi-factor authentication?
Not by name. SOC 2 evaluates organizations against the Trust Services Criteria, which include access control principles rather than naming specific technologies. In practice, however, auditors expect MFA as evidence that access controls are being met, and its absence (especially on administrative accounts) is one of the most common findings that results in a qualified SOC 2 Type II report. Most organizations preparing for SOC 2 treat MFA as effectively required.
Does HIPAA require multi-factor authentication?
The current HIPAA Security Rule requires access controls and audit controls for systems handling electronic protected health information, but it doesn't name MFA as an explicit requirement today. A proposed rule (NPRM published January 2025) would make MFA mandatory for ePHI access, but as of mid-2026 this rule has not been finalized and HHS has indicated final action will not occur until at least July 2027. Organizations handling ePHI can implement MFA now to strengthen their current access control posture and prepare for the pending rule change.
What are the biggest credential security risks enterprises face?
Inconsistent MFA enforcement across accounts and systems remains a leading risk, particularly for companies managing multiple compliance obligations simultaneously. A gap in MFA coverage on even a small subset of accounts (an overlooked admin account, a legacy system, a third-party vendor connection) can be the difference between a clean compliance audit and a qualified finding, and between a protected credential and a compromised one.
How do I get a centralized view of credential hygiene across all employees, including MFA enrollment?
A business password manager with an admin console gives security teams visibility into MFA enrollment status across all employees, alongside password strength and reuse data. Dashlane’s admin console surfaces this in a single dashboard, which supports both day-to-day credential risk management and the audit evidence requests that come up during SOC 2, PCI DSS, and HIPAA assessments.
How do I enforce MFA company-wide with minimal friction?
The most effective approach ties MFA enrollment to the onboarding process rather than treating it as a follow-up task. When MFA is required as part of day-one account setup through a business password manager, employees are enrolled automatically rather than through a separate compliance push. Admin console policies can flag any account that falls out of compliance, giving the security team continuous visibility rather than a periodic audit scramble.
Sign up to receive news and updates about Dashlane