Digital identity is making 100 years of physical ID verification obsolete by encompassing cybersecurity practices into online identification.
Modern, digital replacements for ID cards, passwords, and PIN codes have already arrived. Digital identity is improving authentication, simplifying computing and business practices, and creating a more level playing field for businesses around the world.
What is digital identity?
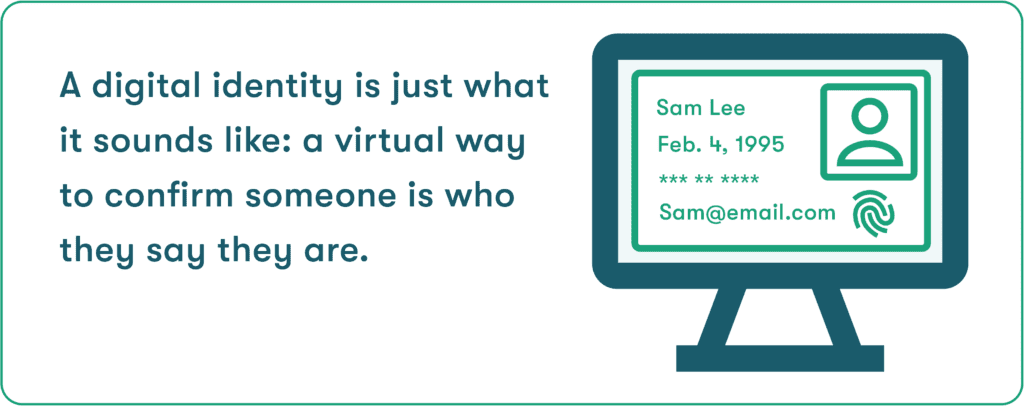
A digital identity (ID) is an electronic representation of information that can be used to positively identify a person. Much like conventional forms of identification, such as driver’s licenses and passports, a digital identity relies on information linked to one individual. Unlike physical IDs, a digital ID can be used to verify identity in both the physical and online realms. Digital identities are established based on:
- Unique attributes like date of birth, government identification numbers, email addresses, and other individual identifiers
- Credentials such as usernames, passwords, and biometric markers like fingerprints that can authenticate device owners when they use their digital IDs
- Digital data that establishes user identification based on a user’s IP address, device information, and location.
Access controls use tools like digital identity certificates and secure online encryption processes to verify identity. Public encryption keys are provided to individuals based on attributes like their username or IP address, allowing them to access data or applications locked by corresponding private encryption keys until a positive identification is completed.
The key elements of digital identity
To better understand the purpose and importance of digital identity, you need to know why it’s being used, how it improves security, and how digital IDs can be safely controlled and distributed.
1. Usage
Instances of fraud and identity theft based on conventional ID formats have coincided with more online accounts for us to track and authenticate, each requiring a strong and unique password to gain access. Digital identification addresses these growing concerns by allowing individuals to authenticate themselves in a consistent, secure way, whether they’re logging in to a digital tool at work, boarding a plane, or entering a restricted facility.
2. Security
Digital identity improves security practices in many ways. The strong authentication process prevents unauthorized account access and helps businesses manage rights and permissions more easily. Digital IDs also improve online privacy and reduce the chances of identity theft based on stolen physical ID information. At the same time, digital identity minimizes fraud by making IDs nearly impossible to fake because they no longer rely on paper documents or cards that can be altered by hand.
3. Centralization
Centralization is an important element of digital identity because it allows the policies and procedures used to create digital IDs to be standardized and managed by one authority, like a large government agency or a trusted company. Centralizing also allows people to use the same digital identity for many different purposes because it steers everyone towards the same standard requirements and practices.
However, the notion of a centralized identity management system, perhaps on a global scale, also raises concerns. Centralization could make it more difficult for individuals to know how their information is being shared or used without their permission, such as through unwanted government surveillance or transferring of personal information between government agencies and private companies.
Additional drawbacks of centralized digital identity might include:
- Computer errors that cause access problems to propagate across multiple accounts and applications
- Overly invasive tracking and analysis of individual online behavior and physical movement
- The implications of a cyberattack when all digital ID information is stored in one place and managed by a single authority
5 benefits of digital identity use
The popularity of digital identification methods will continue to grow as more businesses and individuals experience the benefits, which include:
1. Reduced risk of data breaches
Digital identity practices reduce the risk of data breaches because strong authentication protocols make it harder for hackers to gain unauthorized access. Digital identity solutions also monitor and log activity to detect suspicious activities in real-time. This allows companies or individuals to react quickly and minimize the impact of hacking attempts.
2. Less reliance on humans
Many of the weaknesses found in traditional identification methods are based on a reliance on humans, increasing errors. Digital identity automates authentication processes, making them more efficient and less error-prone. This also applies to the automation of individual processes like password generation and storage, where risky practices like password reuse undermine privacy and security by exposing multiple accounts during a breach.
3. Improved inclusivity
Digital identification creates a level playing field by removing some of the biases associated with physical IDs. Studies have shown that digital IDs improve access to healthcare, education, and jobs in countries that encourage their use and increase gross domestic product (GDP) by 3 to 13%. To experience such positive outcomes, digital identity systems must also be accessible to all and free from any biases or unfair restrictions of their own.
4. Ease of use
When you use a single set of credentials for multiple services, you no longer need to track and remember so many usernames and passwords, which makes your online activities easier and more efficient. Modern identification methods also build on the potential of biometric factors like facial recognition that are difficult to fake and don’t require plastic ID cards or identification codes.
5. Consolidation across different platforms
Consumers and businesses have always had to adapt to many different identity verification systems to complete their transactions. Digital identity creates a more standardized, centrally managed, and universally accepted system. Rather than entering your place of business with an ID card, unlocking your phone using facial recognition, then opening your email with a username and password, digital identity can eventually fold all these activities into one common platform.
Real-world use cases for digital ID
Digital identity isn’t a new concept, but modern technology has now taken universally accepted digital identification practices to new heights. Some useful and intriguing digital identity examples include:
Healthcare: Data privacy and patient identification are essential in the healthcare industry and form the basis of many laws and regulations. Digital identity can be used to verify patients and doctors quickly before sending private healthcare data electronically. As remote care, like telemedicine, evolves, this improved authentication will also help preserve patient identity and confidentiality before and during virtual online visits.
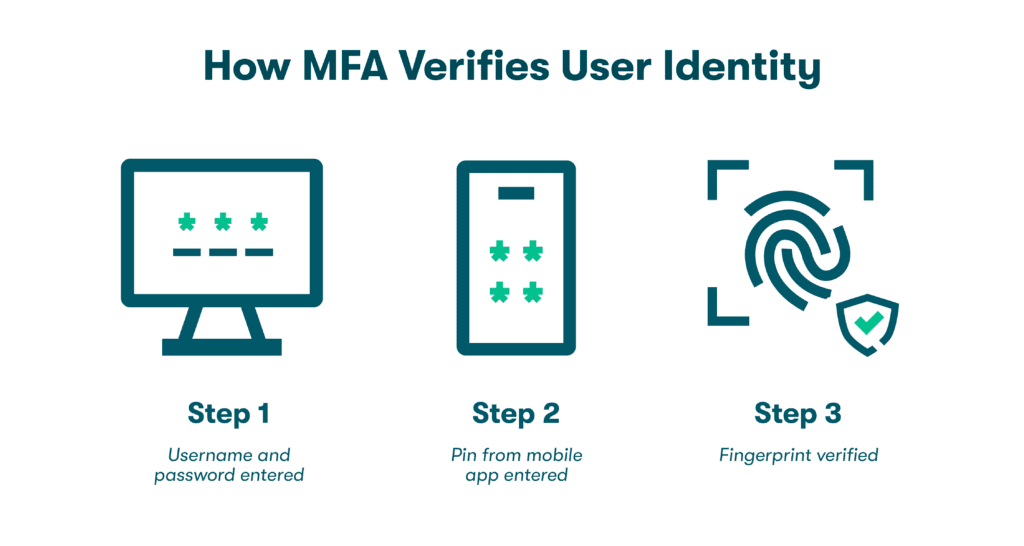
Government: Digital identity examples for government services include immigration processes that streamline identification at borders, fraud-proof voter registration, and heightened authentication practices to prevent tax or unemployment fraud. Most government websites already use 2-factor authentication (2FA) or multifactor authentication (MFA) to improve their cybersecurity, but digital identity spreads these security benefits across a wider variety of physical and online applications.
Finance: With the increased number of online deposits, fund transfers, and sales transactions, it’s no surprise that financial institutions are frequently targeted by hackers. When the identity of buyers and sellers can be verified in real-time, this reduces the chances of payment errors and cybercrimes. Digital identity and asymmetric encryption are also used to ensure cryptocurrency transactions can’t be altered or tampered with.
Employment: Verifying the identity and credentials of prospective employees can be a labor-intensive and time-consuming effort for human resource teams. With a common framework for identification established, employers can limit application fraud and screen candidates more efficiently. This verification process can even carry over to facility and system access using the same digital ID after the employee is hired.
Provisioning: Digital identity as the key to day-one access
When a new employee joins an organization, their digital identity is the mechanism by which access is granted. In a well-structured IAM program, this happens through two integrated processes:
- Single sign-on (SSO) maps the employee’s verified digital identity to a set of applications. Rather than issuing individual credentials for every tool the employee needs, such as corporate email, project management, code repositories, cloud infrastructure, and HR platforms, SSO authenticates the employee once, using their verified identity, and grants access to all authorized applications in a single step. The employee has one credential set; their digital identity determines which systems that credential unlocks.
- SCIM provisioning (System for Cross-domain Identity Management) automates the user account creation process. When the employee is added to the identity provider, their accounts in connected systems are created automatically, with the correct access permissions for their role, department, and seniority. No IT ticket is required per application. No manual account setup introduces delays or errors. The new employee’s digital identity propagates across the organization’s systems in minutes, not days.
Together, SSO and SCIM translate the employee’s digital identity into operational access from their first login, without requiring the employee to manage separate credentials for each system.
Dashlane integrates with major SSO and identity providers, functioning as the credential layer for everything SSO does not cover, like the SaaS tools, vendor portals, and shared accounts that sit outside the SSO perimeter. IT and security teams can provision Dashlane through SCIM alongside other applications, so the password manager itself is part of the day-one identity provisioning flow rather than an afterthought.
Access during tenure: identity as an ongoing access control
A digital identity is not static. As an employee changes roles, joins new projects, or gains additional responsibilities, their access permissions should expand to match and contract when those responsibilities end. This is the principle of least privilege. Essentially, employees should have access to exactly what their current role requires, and nothing more.
In practice, maintaining least-privilege access at scale requires the digital identity layer to connect to an ongoing access governance program:
Role-based access controls tie system permissions to the employee’s role in the identity provider rather than to the individual. When the employee’s role changes, their permissions update automatically across all connected systems, rather than requiring a manual audit of which individual application accounts need to be updated.
Access reviews periodically confirm that each employee’s current access still matches their current responsibilities. Employees who accumulated access during a role transition, project, or temporary assignment retain that access unless it is explicitly reviewed and revoked. Without a structured review process, access sprawl accumulates quietly.
Credential hygiene within the access control layer ensures that the credentials protecting each access point are strong, unique, and not compromised. A digital identity framework that provides correct access permissions but allows employees to protect those accounts with weak or reused passwords leaves the access control layer vulnerable at the authentication point. Dashlane’s admin console connects the credential hygiene layer to the access governance picture. IT teams can see, across all enrolled employees, which credentials protecting business-critical systems are weak, reused, or have appeared in breach data, then remediate those risks before they're exploited.
Deprovisioning: the most neglected phase of the identity lifecycle
Provisioning receives the most attention in most IAM discussions. Deprovisioning, or the removal of access when an employee leaves, is both more consequential and more frequently incomplete.
When an employee departs, their digital identity should be revoked across every system it grants access to. In practice, this rarely happens fully or immediately. Manual offboarding processes miss accounts. Systems outside the SSO perimeter are not automatically notified of the identity change. Shared credentials the employee knew, such as tool logins, service accounts, and shared vendor portals, remain accessible unless the security team identifies and rotates each one.
The gap between access that should have been revoked and access that was actually revoked is one of the most common sources of post-offboarding credential risk. Former employees retain access to SaaS tools, cloud storage, and shared accounts for weeks or months after leaving, not through any malicious configuration, but because the deprovisioning process was incomplete.
Digital identity frameworks with SCIM integration address this at the provisioning layer. When the employee is removed from the identity provider, their connected accounts are automatically deprovisioned. The access revocation propagates to every SCIM-connected system simultaneously, without requiring the IT team to work through a manual checklist of individual applications.
For systems outside the SCIM perimeter, Dashlane’s admin console enables the security team to immediately revoke access to credentials shared with the departing employee. Credentials that were shared individually through Dashlane (rather than through email or Slack) can be revoked in a single admin action.
The combination of SCIM-automated deprovisioning for identity-provider-connected systems and Dashlane admin console revocation for shared credential sets gives organizations coverage across both layers of the offboarding access problem, closing the gap that manual processes reliably leave open.
The current trends and future of digital ID
The demand for digital identity is evident, with key trends pointing to widespread acceptance and adoption of these systems.
More national digital ID initiatives
The coming years will see more digital ID initiatives at the state, national, and international levels. In 2021, the European Union (EU) launched a program designed to create secure digital identities for all Europeans, and other regions have established similar programs. These high-profile programs will speed up worldwide adoption. The United Nations has also called for universal digital identities by 2030.
Digital licenses and IDs
Several U.S. states are now exploring or have already launched digital or mobile driver’s license programs. These digital IDs are already being issued in countries including Argentina, the United Kingdom, and Denmark. ePassports are also gaining momentum. They include a secure electronic chip with a parallel digital identity to prevent forgery and a biometric identifier in the form of a digital image.
Greater demand for security and trust
Consumers, taxpayers, and voters are in favor of convenient online options, but not when they come at the expense of cybersecurity. Public demand for higher levels of security and trust is quickly moving us toward digital identity and guiding those who create the norms and practices.
Commitment to privacy
Privacy is a must-have for the widespread adoption of digital identification. This starts with consent for the release of any information used to create a digital identity and includes safeguards to make sure this information isn’t shared. The zero-knowledge architecture used by security-first password managers is an example of how technology can be used to improve customer privacy.
Digital identity is a concept that brings together advanced cyber tools like multifactor authentication (MFA), data encryption, single sign-on (SSO), and secure information sharing to replace familiar physical IDs and create a universally recognized system for multi-purpose identification. These same advanced features, coupled with convenient password generation and autofill capabilities, make password managers indispensable.
Frequently asked questions
What does workforce-wide credential risk visibility mean for enterprise security?
In the context of digital identity and workforce IAM, it means the security team can see the current state of every employee’s business credential set. This means they can see not just what systems they are provisioned for, but whether the credentials protecting those systems are strong, unique, and free of known compromises. Digital identity frameworks handle the provisioning and access control layer. Credential risk visibility fills the gap between “has access” and “is that access actually secure,” surfacing weak passwords, reuse across accounts, and dark web breach matches across all enrolled employees in a single admin console view.
How do enterprises manage and reduce credential-based security risk?
The most effective approach operates at the same three lifecycle stages as workforce digital identity: provisioning (ensuring day-one credentials are strong and unique, stored in a managed vault rather than self-managed), access during tenure (monitoring credential health continuously and remediating weak or compromised credentials before they're exploited), and deprovisioning (revoking credential access fully and immediately at offboarding, across both SCIM-connected systems and shared credential sets managed through a business password manager).
How do I give new employees secure credential access from day one?
SSO and SCIM provisioning handle the identity-provider-connected application layer automatically. Dashlane is provisioned alongside those applications through SCIM, so the employee’s password manager, with the organization’s shared team credentials already accessible, is live from their first SSO login. Credentials outside the SSO perimeter, such as vendor portals, shared tools, and third-party SaaS without SSO connectors, are provisioned through the Dashlane admin console to the appropriate groups. The employee arrives on day one with access to everything they need, stored in a managed environment, without receiving a credential over email.
What is the easiest enterprise credential security platform to roll out at scale?
Dashlane deploys through existing SSO and SCIM infrastructure, which means rollout follows the same path as any other SSO-connected application deployment. Employees authenticate with their existing corporate SSO credentials, with no separate Dashlane master password. Dashlane is provisioned automatically when employees are added to the identity provider and revoked when they're removed. For organizations with an existing IAM program, adding Dashlane is an extension of the same workflow.
What are the biggest credential security risks facing enterprises today?
Incomplete deprovisioning remains one of the most under-addressed. Digital identity frameworks handle SSO-connected account revocation well, but credentials employees stored in unmanaged locations—such as browser password managers, personal vaults, and shared spreadsheets—aren't covered by SCIM deprovisioning. Former employees retain access to systems protected by credentials they memorized or stored outside the managed environment. Combining SCIM deprovisioning with a business password manager that covers the non-SSO credential set closes this gap systematically rather than relying on manual credential audits at every offboarding.
How do security teams remediate compromised credentials at scale?
Effective credential remediation at the workforce IAM level requires three things: automated detection of compromised or at-risk credentials (dark web monitoring and a credential health dashboard), centralized controls to act on those signals without coordinating individually with each employee (admin console remediation prompts), and an audit trail documenting each remediation action for compliance purposes. Dashlane’s enterprise platform provides all three, integrated with the SCIM-based provisioning and deprovisioning lifecycle so that credential risk management is part of the identity governance workflow rather than a separate program.
Sign up to receive news and updates about Dashlane