We're giving you a list of the top 10 trends for commonly exposed passwords. Why? Because industry estimates state that the average person has 100 or more passwords. Unsurprisingly, this often leads to creating easy, memorable passwords that follow a popular theme.
But be careful: The more popular and easy-to-guess your passwords are, the more susceptible you (and possibly your workplace, by extension) are to cybercriminals.
Check out the list below to see if any of your passwords fit into these popular categories.
10 top trends for commonly exposed passwords
In an analysis of 3.3 billion distinct identity records, SpyCloud identified 10 trends for commonly exposed passwords:
- Autumn / fall / leaves
- US Open / tennis / grand slam
- Cat / kitten / kitty
- Olympics / Paris Olympics / torch
- Zelda / Nintendo / Ganondorf
- Taylor Swift / Swiftie / Eras / Tortured Poets
- Super Mario / Mario / Donkey Kong
- Fortnite / Battle Royale / bus / storm / yeet
- Deadpool / Chimichanga / Wolverine / Marvel
- Charlie XCX, Brat, brat summer
Pop culture references clearly dominate this list, spanning from sports to music to video games and beyond. However, none could reach the popularity of autumn-themed passwords.
Top 4 most common passwords
Those are the most popular categories for commonly exposed passwords, but what about the most common passwords overall? Well, the most used passwords should come as a shock to no one:
- 123456
- 111111
- Admin
- Qwerty
Number sequences continue to be popular choices, with "Admin" often being favored for certain work accounts and "Qwerty" being a go-to option both personally and professionally.
Password security takeaways
Here are some lessons we can learn from these top 10 password trends and top 4 most common passwords:
- Seasonal and pop culture references are not secure options. You should always use randomized letters, numbers, and symbols instead.
- Even if your password doesn’t use 1 through 9 in order, choosing numbers in a sequence makes your password incredibly easy for hackers to guess.
- Alphabetical sequences and dictionary words are just as bad. “Admin” and “qwerty,” for example, are very overused and easy to guess.
Don’t be surprised if some variation of one of your passwords made either list above. But if your password isn’t part of the top trends, that doesn’t mean you’re in the clear either.
Hackers will be able to guess your password much more easily if:
- Your password is too short and simple. This could look like a single word followed by a number or an exclamation point or a single numerical phrase like a birthdate.
- Your password is reused across multiple accounts. This practice should be avoided because once a hacker accesses one of your accounts, they’ll be able to access all the accounts that share that password and guess any similar ones.
- Your password contains personal information. Using birth dates, personal information, or a street address isn’t suitable for a strong password.
My password falls into one of the trends. What now?
Weak and reused passwords are one of the most common reasons data breaches occur. Luckily, there are some easy ways you can improve the security of your passwords.
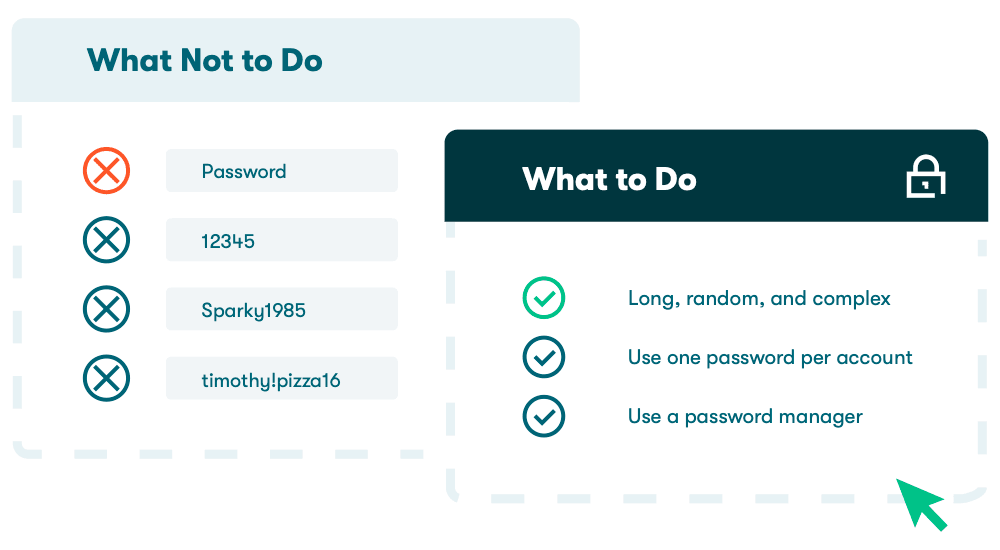
The first thing you should do after discovering your password has made this list is to change your password to something long, unique, and complex. Here are some tips for how to create a strong password that won’t show up on a “common password trends list” ever again:
- Use a password generator to create long, complex, and random passwords
- Never use the same password for more than one account
- Store each password in a password manager
What might happen if I use one of these passwords?
If you have easy-to-guess passwords, you might not think you’re a target, but you’re at a higher risk of a data breach. When your password is stolen on one account, hackers can easily access other accounts, including banking and financial information, which can lead to credit card fraud and identity theft.
These crimes aren’t only dangerous to your finances and personal information; they’re also a pain to resolve. The Federal Trade Commission estimates that recovering from identity theft can take six months or 200 hours of work.
What these trends look like across an entire workforce
If you find yourself using or witnessing weak and reused passwords at work, the individual habits described above become a collective risk problem. The trends on this list don't stay isolated to one person's accounts. They spread across organizations in predictable patterns, and that predictability is exactly what attackers exploit.
“Admin,” the third most common password overall, is particularly telling for business environments. It's a default credential on legacy systems, internal tools, and shared accounts that IT teams inherit and often never update.
A credential health audit will typically surface the same handful of weak patterns (seasonal variations, company-name derivatives, simple numeric sequences) appearing independently across dozens or more employee accounts. And when the same weak password secures a corporate email account, a SaaS tool, and a personal streaming service, a breach of any one of them exposes all three.
Ben Silver, Manager of IT Support at BentoBox, encountered this scale directly when his organization deployed Dashlane:
“I've been using the internet since I was 13, and I've been in numerous data leaks. When I started using Dashlane, I could easily see that I had 600 reused passwords. But more importantly to me, I could quickly see which critical passwords had been leaked. For instance, I need to know right away if someone has my bank password.”
Six hundred reused passwords is a single person's digital history. Multiply that by a workforce, even a small one, and the aggregate credential risk is not six hundred weak points but potentially tens of thousands, most of them invisible without the right tooling.
How Dashlane's admin console flags weak and reused passwords at the organization level
A business password manager with admin console controls moves credential risk management from the individual to the organization. Instead of discovering that one employee had 600 reused passwords after they join Dashlane, a security team gets a live view of credential health across every enrolled employee, continuously rather than only at onboarding.
Dashlane's admin console surfaces what the trends above look like in aggregate:
- Reuse rate across the workforce, tracked through Password Health. Not just whether one employee reused passwords, but what percentage of the organization has reused passwords, and which accounts share credentials with others, including the most sensitive ones.
- Weak password counts by employee and by account, also tracked through Password Health. The admin console identifies which employees have credentials below the minimum strength threshold and, critically, which accounts those weak passwords are protecting. A weak password on a rarely used SaaS trial is a different risk from a weak password on the corporate VPN or SSO login.
- Dark web breach matches for the entire verified domain, surfaced through Dark Web Insights. When an employee email address on the organization's domain appears in breach data, even for employees who have not yet created a Dashlane account, the alert appears in the admin console. The security team sees it first, rather than waiting for the employee to notice.
The Ben Silver experience above—discovering the scale of the problem and immediately knowing which critical accounts were at highest risk—is what Dashlane's admin console makes available to the IT team, not just to the individual user. And it's available across the entire organization rather than one vault at a time.
For organizations where these trends are showing up in employee password practices, a business password manager is the fastest path from invisible risk to managed, policy-compliant credential hygiene.
Frequently asked questions
What are the biggest credential security risks facing enterprises?
Password reuse and predictable patterns remain the leading risks. The trends on this list (seasonal references, pop culture variants, simple sequences) are exactly the credentials that credential stuffing campaigns test first. When employees apply the same patterns to corporate accounts that they use elsewhere, a breach of any third-party site becomes a potential breach of corporate systems. The risk is compounded by the fact that most organizations have no visibility into which employees are using these patterns until after a breach surfaces the evidence.
What does workforce-wide credential risk visibility mean for enterprise security?
It means a live, continuous view of the actual passwords employees have in use, not a self-reported survey or a one-time audit result. Workforce-wide credential risk visibility shows which employees have weak passwords, which have reuse across accounts, which credentials have already appeared in dark web breach data, and which high-value accounts (corporate email, VPN, SSO) are protected by credentials that fall into the predictable patterns described above. For a security team, this view replaces the manual audit cycle with continuous monitoring.
How do I get a centralized view of credential hygiene across all employees?
A business password manager with an admin console aggregates credential health data across all enrolled employees in a single dashboard. Dashlane's admin console shows password strength scores, reuse counts, weak password locations, and more, all in one place. The view updates continuously rather than periodically, and remediation can be triggered directly from the console without a separate helpdesk workflow.
How do I enforce password security policies company-wide with minimal friction?
The most effective approach makes compliant behavior the default. When a password manager generates passwords automatically, employees don't create seasonal or pop culture passwords in the first place. The generator applies all the rules described above every time, without requiring the employee to think about it. Policy minimums set in the admin console surface credentials that fall below the threshold and can trigger automated remediation prompts to employees. For organizations where weak and reused passwords are a known problem, this replaces the policy-document approach with an enforcement mechanism that operates in the background of every new credential creation.
What's the difference between reactive and proactive credential security?
Reactive credential security discovers weak or compromised passwords after they've been exploited. A breach is confirmed, the affected credentials are reset, and the incident is closed. Proactive credential security surfaces the weak and reused passwords before exploitation through credential health dashboards that flag the patterns described above, and dark web monitoring that alerts the security team when any employee credential appears in breach data. The difference is whether the security team acts before an attacker uses the credential or after.
Sign up to receive news and updates about Dashlane